Mechanism of Death: EO 14306 & OMB M-26-05
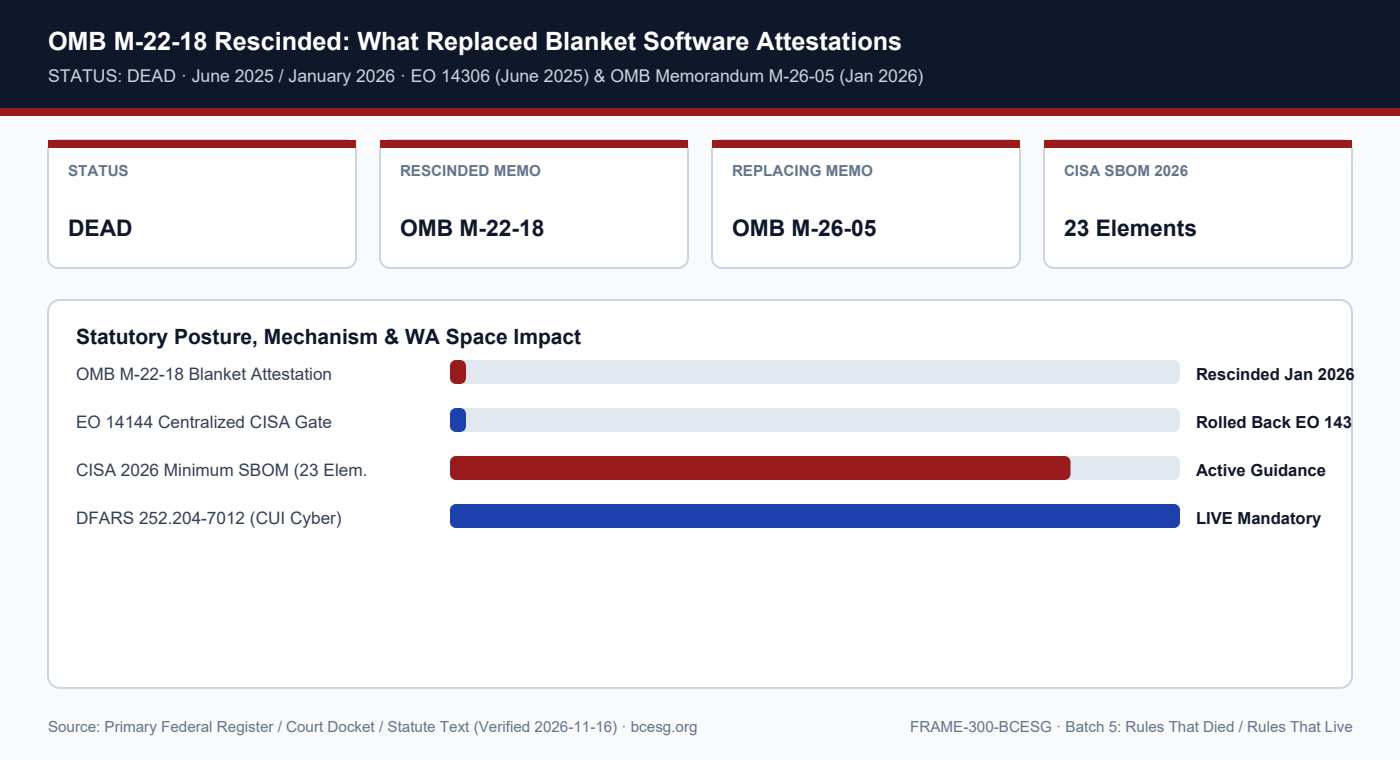
In January 2025, EO 14144 sought to tighten EO 14028 by requiring machine-readable third-party software security attestations routed to CISA. In June 2025, EO 14306 rolled back those centralized CISA validation mandates. In January 2026, OMB Memorandum M-26-05 formally rescinded M-22-18.
As a result, Washington mission-software and ground-system vendors no longer face a single blanket OMB M-22-18 self-attestation form for every federal sale.
- OMB M-22-18 and M-23-16 blanket self-attestation regime is rescinded.
- EO 14306 eliminated centralized CISA attestation submission mandates.
- Agency-specific risk-based clauses and NIST SP 800-218 (SSDF) remain active.
| Software Security Instrument | 2025–2026 Action | Current Status |
|---|---|---|
| OMB M-22-18 Blanket Attestation | Rescinded by OMB M-26-05 (Jan 2026) | DEAD |
| EO 14144 Centralized CISA Validation | Rolled back by EO 14306 (June 2025) | DEAD |
| CISA 2026 SBOM Minimum Elements | Expanded to 23 elements | LIVE (Guidance / Contract Spec) |
| NIST SP 800-218 (SSDF) | Retained as baseline engineering standard | LIVE (Reference Standard) |
What Replaced It: CISA 2026 23-Element SBOM & Agency Risk Terms
OMB M-26-05 shifts federal software assurance to agency-led, risk-based procurement. Meanwhile, CISA published its updated 2026 Minimum Elements for a Software Bill of Materials (expanding from 7 to 23 elements), and DoD/NASA contracts still enforce DFARS 252.204-7012 and mission-critical SBOM deliverables.